PHANTAQSM
EU-sovereign managed SSH honeypot deception for regulated buyers
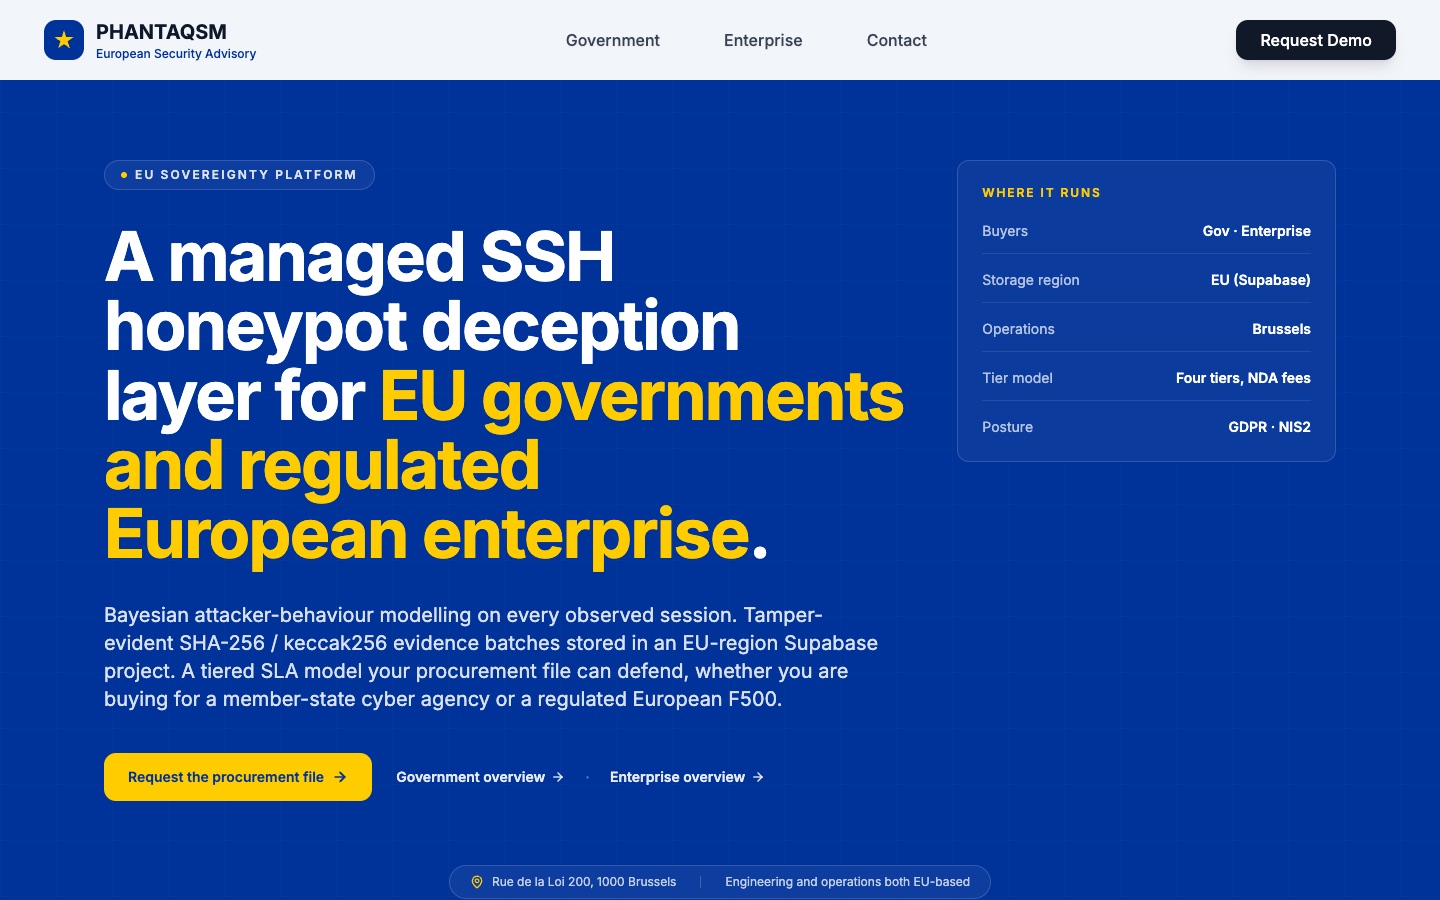
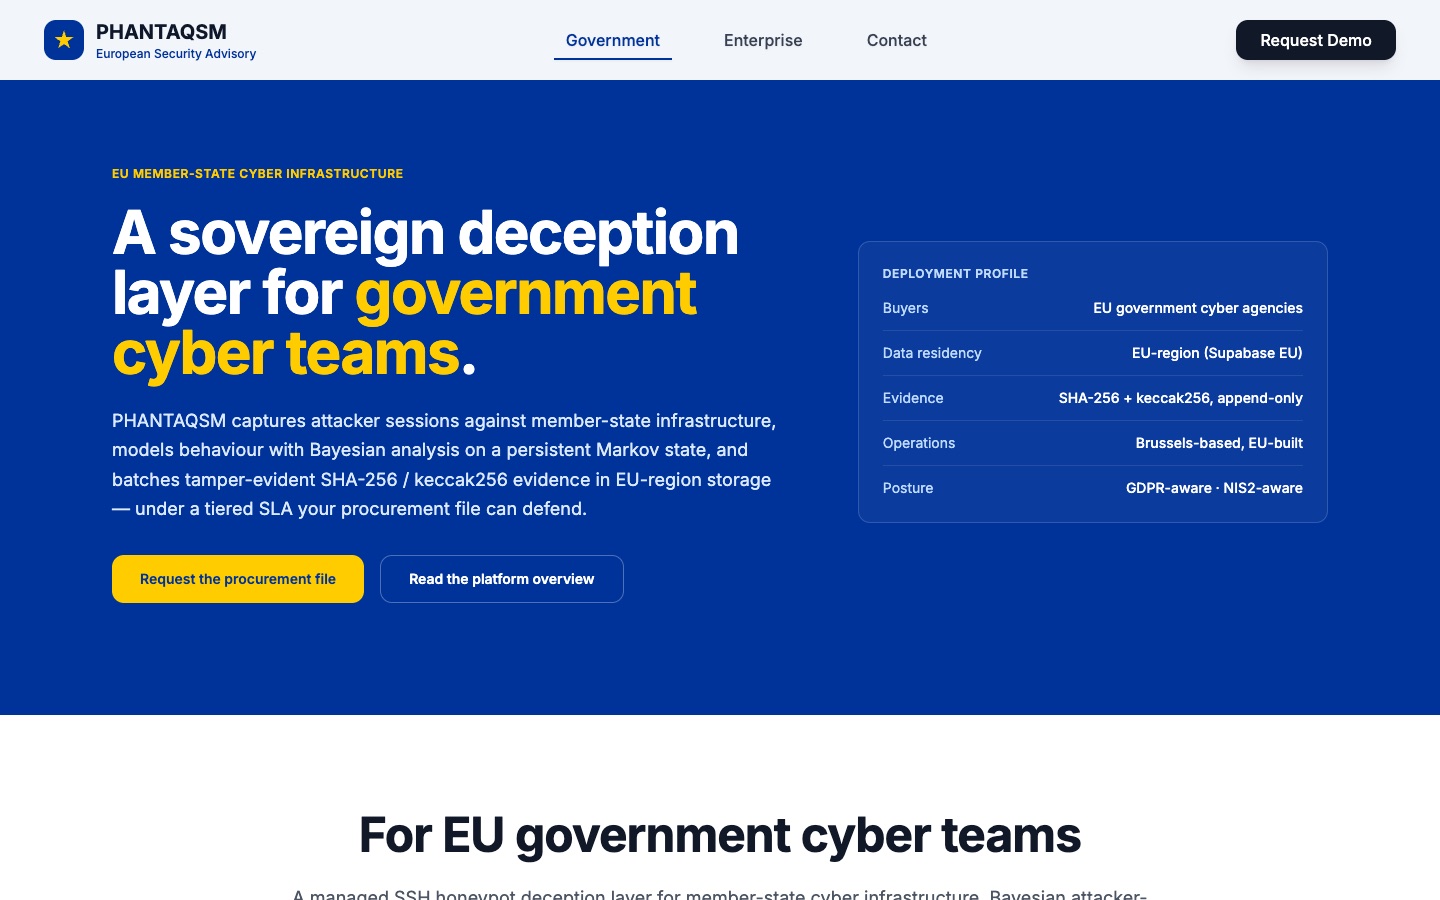
For: Procurement officials and cyber teams at EU member-state agencies (national CSIRTs, interior, defence and digital-affairs ministries), and CISOs at regulated European enterprises in banking, energy and critical infrastructure.
PHANTAQSM puts decoy SSH environments in front of attackers so that adversaries engage the decoy while production systems stay untouched. Every observed session is captured and analysed, producing evidence a security team can act on and defend.
Each session feeds a Bayesian model that keeps a working hypothesis of what the attacker is trying to do, with confidence weights stored as auditable session metadata. The session payload is hashed with SHA-256 (a keccak256 variant is available) and batched into an append-only evidence log.
Sovereignty is a design requirement, not an add-on. Evidence and customer data live in an EU-region Supabase project with no transatlantic data movement by default, and engineering and operations are EU-based. The honeypot environment never ingests customer or employee personal data, and logging is designed with GDPR and NIS2 in mind.
There are two procurement tracks: member-state cyber agencies (national CSIRTs and the cyber units of interior, defence and digital-affairs ministries) and regulated European enterprise in sectors such as banking, energy and critical infrastructure. Buyers receive a procurement file with the tier matrix, SLA-breach policy, data-flow diagram and cryptographic scheme under NDA.
4
Service tiers, Bronze to Classified
1 hour
First-acknowledgment response time at Classified tier
What it does
Managed SSH honeypot (tarpit) environments that keep attackers away from production systems
Bayesian attacker-behaviour modelling on every session, backed by a persistent Markov model state
Tamper-evident SHA-256 / keccak256 evidence batches in an append-only log
EU-region data residency by default, configurable on request
Four service tiers (Bronze, Silver, Gold, Classified) with published first-response times from one business day down to one hour
Honeypot environments per tier: up to 3, 10 or 30, or scoped by engagement
Customer portal showing tier, open SLA incidents and environment uptime
Procurement file under NDA with threat model, data-flow diagram and SLA-breach remediation policy
How we architected it
- Next.js 15
- React 18
- TypeScript
- Tailwind CSS
- Radix UI
- Framer Motion
- Supabase (Postgres, Auth)
- ethers v6
- Zod
- Vitest
- Vercel
- Hetzner Cloud (planned worker host)
- 01
Next.js 15 App Router site and customer portal on Vercel (Frankfurt region), with Zod validation on every API route
- 02
Supabase EU-region Postgres holds honeypot sessions, evidence hashes and the Markov model state; row-level security and session-scoped auth for tenant isolation are on the hardening roadmap
- 03
Honeypot core in TypeScript, kept separate from the web app: SSH tarpit listener, honeypot manager, Bayesian classifier, Markov model updater, feedback scheduler and adaptive learning engine
- 04
Evidence anchoring hashes session payloads with SHA-256 and keccak256 (via ethers v6) into append-only batches
- 05
The worker is planned as a non-root Node 20 container on Hetzner Cloud eu-central, writing through a dedicated database role
- 06
A health endpoint reports database reachability, version and region; Sentry, pino and Better Uptime are planned for SLA-grade observability
- 07
Accessibility target is EN 301 549 and WCAG 2.2 AA, the EU public-sector procurement baseline
Want something built like this?
Every build runs the same five gates: spec, architect, build, review, ship. It starts with a 48-hour audit.